Hello,
I am Samuel…
I work around
Cybersecurity Leadership,
Privacy and Technology Regulation,
Capacity building at scale.
I strongly believe that “Security isn’t a wall we build around people. It’s a skill you build with them.“
“If the axe is dull and its edge unsharpened, more strength is needed, but skill will bring success.”
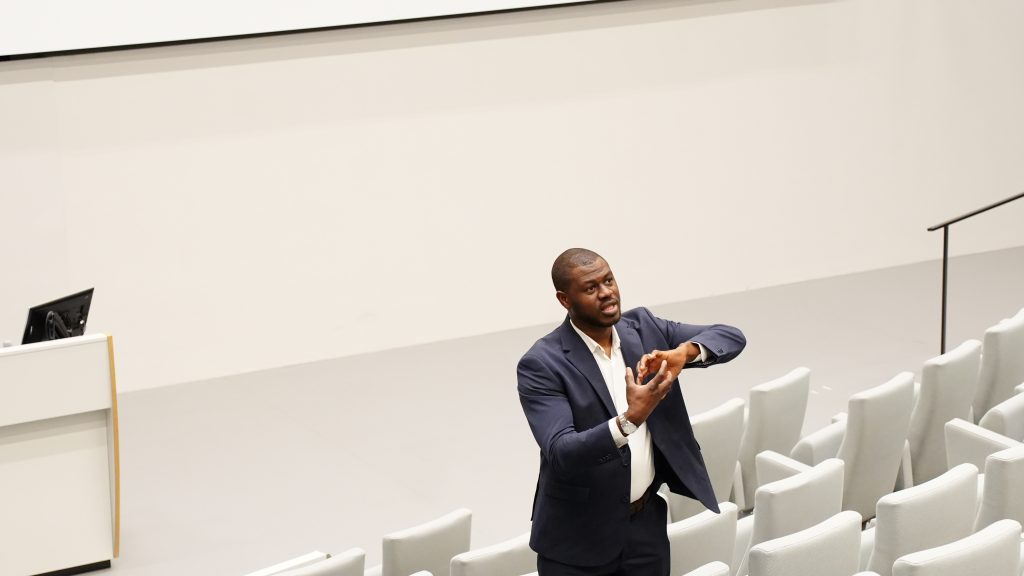
Training and capacity building: 23,000+ participants
I’m passionate about teaching, designing and delivering practical cybersecurity training for technical, policy, governance and community audiences. Through Google supported digital-skills programmes, I have reached more than 23,000 participants over four years. I turn complex cyber-risk topics into clear, usable actions, using needs assessment, curriculum adaptation, practical exercises and follow-up, so that people and organisations can build lasting digital resilience
Research
I’m also committed to academic research with a focus on what happens when EU law places non-delegable responsibility for digital operational resilience on asset-light, cross-border European financial institutions, payment institutions and electronic-money institutions, that depend heavily on outsourced cloud, software and financial infrastructure, while the technical control, evidentiary access and containment authority needed to discharge that responsibility sits with infrastructure providers the regulated entity does not control?
Security leadership and governance
In my daily job, I provide CISO-level security strategy, governance and leadership, grounded in legal and regulatory expertise. I report to executives, engage stakeholders and manage external counsel. I write security policy, standards and controls, and prepare organisations for audit against GDPR, DORA, NIS2, PCI DSS, ISO 27001, SOC 2 and TISAX, turning regulatory requirements into practical, auditable programmes that fit the business.
It would be nice to meet you. Let’s connect!
© 2026